Blog's Page
 Blog's Page
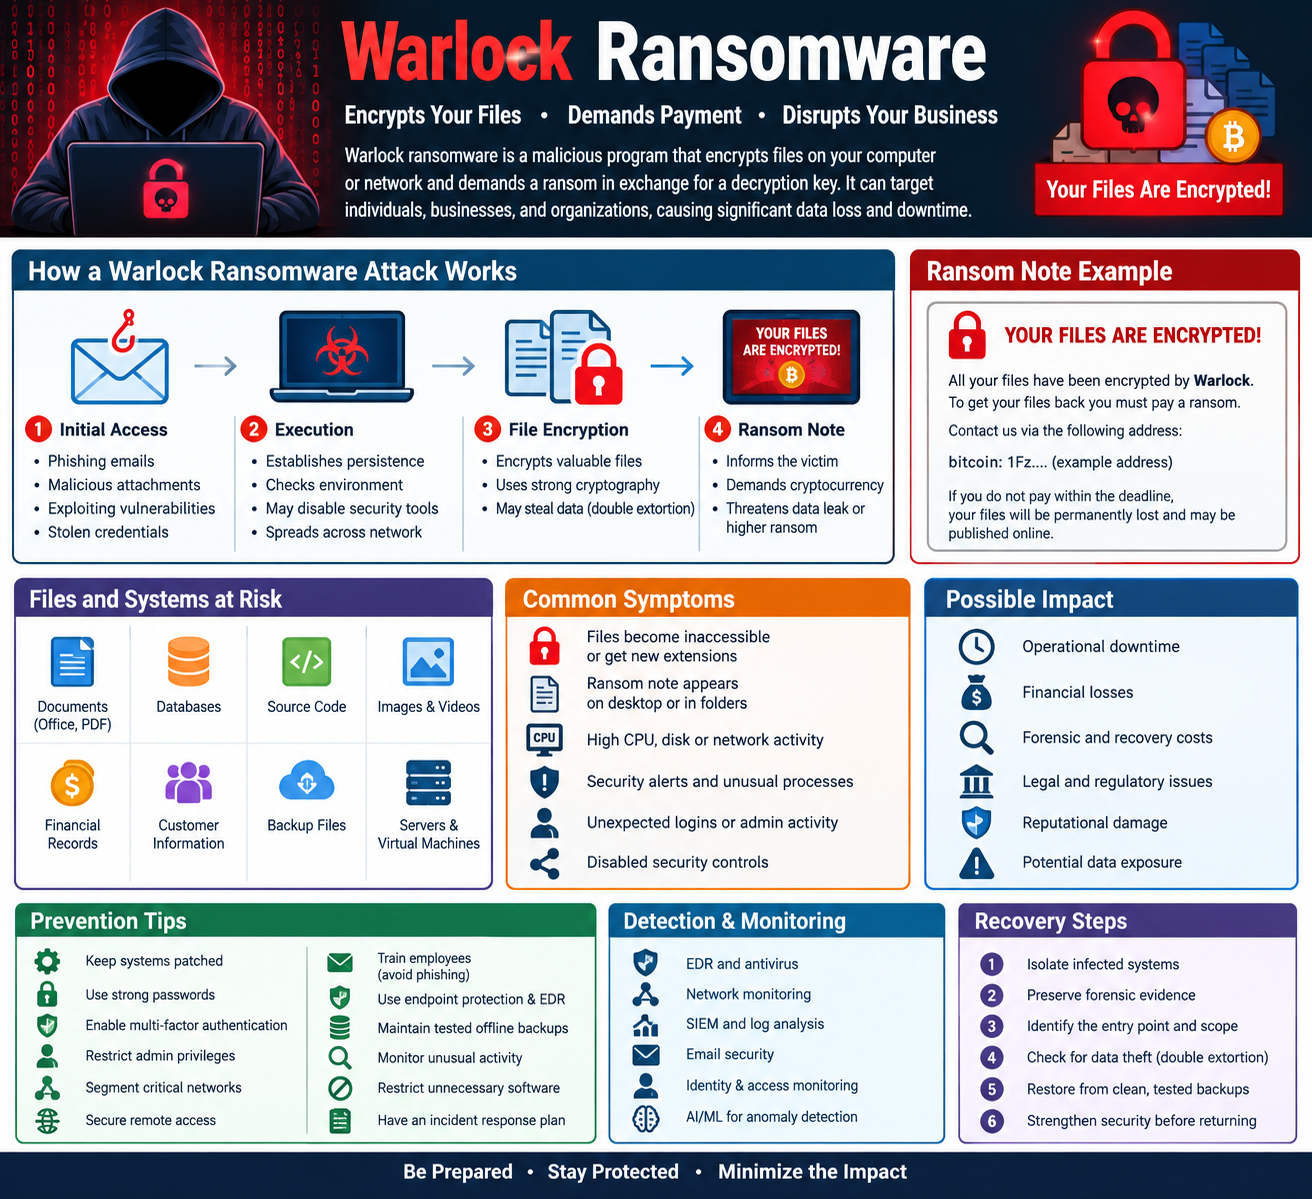
Warlock Ransomware Is A Malicious Ransomware Threat Designed To Compromise Computers And Networks, Encrypt Valuable Files, And Demand Payment From Victims In Exchange For A Purported Decryption Key. Like Other Modern Ransomware Families, Warlock Can Cause Significant Operational Disruption By Making Documents, Databases, Backups, And Other Business-critical Resources Inaccessible. Organizations Are Particularly Vulnerable Because A Successful Attack Can Affect Not Only Individual Endpoints But Also Shared Network Resources And Connected Systems.
Warlock Ransomware Belongs To The Broader Category Of File-encrypting Malware. Its Primary Objective Is To Deny Victims Access To Their Data By Applying Encryption To Targeted Files. After Encryption, Attackers Typically Leave A Ransom Note Explaining What Happened And Providing Instructions For Contacting The Threat Actors Or Making A Payment. The Criminals Generally Promise To Provide A Decryption Solution After Payment, Although There Is No Guarantee That Victims Will Receive A Working Decryptor.
Ransomware Such As Warlock Can Target Individuals, Companies, Educational Institutions, Government Organizations, And Other Environments Containing Valuable Information. The Impact Is Not Limited To The Encrypted Files Themselves. System Downtime, Incident-response Expenses, Data Recovery, Legal Obligations, Reputational Damage, And Potential Data Exposure Can Make A Ransomware Incident Considerably More Expensive.
Ransomware Infections Can Originate From Several Attack Vectors. Phishing Emails Are One Of The Most Common Mechanisms Used By Ransomware Operators. An Attacker May Send A Convincing Message Containing A Malicious Attachment Or Link. If A Recipient Opens The Attachment Or Visits The Malicious Destination, Malware May Be Delivered To The System.
Another Possible Route Is Exploitation Of Vulnerable Internet-facing Services. Attackers Continuously Scan The Internet For Systems Containing Unpatched Vulnerabilities, Weak Authentication, Exposed Remote-access Services, Or Misconfigured Applications. Once An Attacker Obtains An Initial Foothold, They May Attempt To Move Deeper Into The Environment.
Compromised Credentials Can Also Provide An Entry Point. Stolen Passwords Obtained Through Phishing, Credential-stealing Malware, Password Reuse, Or Data Breaches May Allow Attackers To Access Corporate Systems Without Immediately Triggering Traditional Malware Defenses.
Once Ransomware Reaches A Target System, Its Behavior Can Involve Several Stages. The Malicious Program May Establish Persistence, Inspect The Environment, Identify Valuable Files, And Prepare The System For Encryption. Depending On The Attacker's Objectives, The Malware May Also Attempt To Disable Security Software Or Interfere With Recovery Mechanisms.
Attackers May Use Legitimate Operating-system Utilities During Different Stages Of An Intrusion. This Technique Can Make Malicious Activity More Difficult To Distinguish From Normal Administrative Operations. Consequently, Ransomware Defense Should Not Depend Exclusively On Identifying A Particular Executable File.
The Central Function Of Ransomware Is Encryption. Warlock Ransomware May Search Storage Locations For Files That Are Likely To Contain Valuable Information, Such As Documents, Spreadsheets, Databases, Archives, Images, Source Code, And Project Files.
Modern Ransomware Commonly Uses A Combination Of Cryptographic Techniques. Symmetric Encryption Can Provide Efficient Encryption Of Large Quantities Of Data, While Asymmetric Cryptography Can Protect The Keys Required For Decryption. This Approach Makes Recovery Difficult Without Access To The Attacker's Cryptographic Material.
The Exact Encryption Implementation And Affected File Extensions Should Be Investigated From A Verified Malware Sample Rather Than Assumed From The Ransomware's Name Alone.
After Completing The Encryption Process, Ransomware Generally Creates A Ransom Note. The Note Informs The Victim That Files Have Been Encrypted And Usually Provides Instructions For Contacting The Attackers.
A Ransom Demand May Specify A Cryptocurrency Payment And Sometimes Includes A Deadline. Attackers May Threaten To Increase The Ransom, Delete Decryption Keys, Or Publish Stolen Information If Payment Is Not Made.
Organizations Should Preserve Ransom Notes As Evidence. They Can Provide Valuable Information For Incident Responders And Malware Researchers.
Modern Ransomware Operations Frequently Combine Encryption With Data Theft. This Is Commonly Called double Extortion.
In Such An Operation, Attackers First Obtain Sensitive Information From The Victim And Subsequently Encrypt Systems Or Files. They Then Threaten To Publish The Stolen Information Unless The Organization Pays.
This Significantly Changes The Incident-response Process. Restoring Encrypted Files From Backups May Solve The Availability Problem, But It Does Not Necessarily Solve The Confidentiality Problem If Sensitive Information Was Stolen.
Potentially Valuable Targets Include:
Microsoft Office Documents
PDF Files
Databases
Source-code Repositories
Images And Videos
Financial Records
Customer Information
Backup Files
Virtual-machine Data
Research Documents
Email-related Data
Network Shares
Servers Are Particularly Important Because Compromising A Central Server Or Shared Storage System Can Affect Many Users Simultaneously.
A Warlock Ransomware Infection May Produce Several Noticeable Symptoms. Files May Suddenly Become Inaccessible Or Appear With Unfamiliar Extensions. A Ransom Note May Appear On The Desktop Or Inside Affected Directories.
Users May Also Notice Unusual CPU, Disk, Or Network Activity During Encryption. Security Products May Generate Alerts Associated With Suspicious Processes, Unusual File Modifications, Credential Abuse, Or Attempts To Interfere With System Recovery.
Other Warning Signs Can Include Unexpected Administrative Activity, Disabled Security Controls, Unexplained Account Logins, And Unusual Access To Network Shares.
The Consequences Of Ransomware Can Be Severe. An Organization May Experience Operational Downtime Because Employees Cannot Access Essential Systems. Hospitals, Financial Institutions, Manufacturers, Universities, And Government Organizations Can Be Particularly Affected Because Their Operations Often Depend Heavily On Digital Infrastructure.
Financial Losses Can Include Recovery Costs, Forensic Investigations, Infrastructure Replacement, Business Interruption, Legal Expenses, Regulatory Requirements, And Potential Customer Compensation.
Effective Detection Requires Multiple Security Layers. Endpoint Detection And Response (EDR), Antivirus Systems, Network Monitoring, SIEM Platforms, Email Security, And Identity Monitoring Can Work Together To Identify Suspicious Behavior.
Security Teams Should Monitor For Large-scale File Modifications, Unusual Process Execution, Abnormal Authentication Activity, Suspicious PowerShell Or Command-line Activity, Unauthorized Access To Network Shares, And Unexpected Deletion Of Backups.
Behavior-based Detection Is Particularly Valuable Because Ransomware Variants Can Change Their Filenames, Hashes, And Other Static Characteristics.
If Warlock Ransomware Is Suspected, The Affected Systems Should Be Isolated From The Network As Quickly As Practical. Isolation Helps Prevent Further Encryption And Limits Potential Lateral Movement.
Organizations Should Preserve Forensic Evidence Instead Of Immediately Deleting Suspicious Files. Security Teams Should Identify The Initial Entry Point, Determine Which Accounts And Systems Were Compromised, Assess Whether Data Was Stolen, And Establish The Scope Of The Incident.
Incident Responders Should Also Inspect Authentication Logs, Endpoint Telemetry, Firewall Logs, Email Records, VPN Activity, And Other Available Evidence.
Reliable Backups Are One Of The Most Important Defenses Against Ransomware. Organizations Should Maintain Multiple Backup Copies, Including At Least One Backup That Is Isolated Or Otherwise Protected From Routine Network Access.
Backups Should Be Tested Regularly. Simply Having A Backup Does Not Guarantee Successful Recovery; Restoration Procedures Must Be Verified.
A Robust Recovery Strategy Should Include Documented Recovery Priorities, Backup Validation, Offline Or Immutable Copies, And Periodic Restoration Exercises.
Organizations Can Reduce Ransomware Risk Through Several Measures:
Keep Operating Systems And Applications Patched.
Use Strong, Unique Passwords.
Implement Multi-factor Authentication.
Restrict Administrative Privileges.
Segment Critical Networks.
Secure Remote-access Services.
Train Employees To Recognize Phishing.
Deploy Endpoint Protection And EDR.
Maintain Tested Offline Or Immutable Backups.
Monitor Unusual Authentication And File Activity.
Restrict Unnecessary Software Execution.
Maintain A Formal Incident-response Plan.
AI And Machine Learning Can Improve Ransomware Detection By Identifying Abnormal Behavior. For Example, A Machine-learning System Can Learn Normal File-access Patterns And Detect Sudden Increases In File Modifications.
Models Can Also Analyze Process Behavior, Network Traffic, Authentication Events, And Endpoint Telemetry. Techniques Such As Anomaly Detection, Random Forest, Gradient Boosting, Autoencoders, And Deep-learning Models Can Be Incorporated Into Security Monitoring Systems. However, AI Should Complement Rather Than Replace Traditional Security Controls.
Warlock Ransomware Represents The Broader And Continually Evolving Ransomware Threat Landscape In Which Attackers Seek To Disrupt Systems, Encrypt Valuable Information, And Potentially Steal Sensitive Data. Defending Against Such Attacks Requires A Layered Security Strategy Rather Than Reliance On A Single Antivirus Product.
Organizations Should Prioritize Vulnerability Management, MFA, Least-privilege Access, Network Segmentation, Endpoint Monitoring, Employee Awareness, And Resilient Backups. When An Infection Occurs, Rapid Isolation, Forensic Investigation, Containment, And Carefully Validated Recovery Are Essential.
Most Importantly, Organizations Should Prepare before A Ransomware Incident Occurs. A Tested Backup And Recovery Plan, Continuous Security Monitoring, And A Practiced Incident-response Procedure Can Dramatically Reduce The Operational Impact Of A Successful Ransomware Attack.
Step 1: Boot Into Safe Mode
Restart Your PC And Press F8 (or Shift + F8 For Some Systems) Before Windows Loads.
Choose Safe Mode With Networking.
Safe Mode Prevents Most Malware From Loading.
Press Win + R, Type appwiz.cpl, And Press Enter.
Sort By Install Date And Uninstall Unknown Or Recently Added Programs.
Use A Trusted Anti-malware Tool:
Malwarebytes – https://www.malwarebytes.com
Screenshot Of Malwarebytes - Visit Links
Microsoft Defender – Built Into Windows 10/11
HitmanPro, ESET Online Scanner, Or Kaspersky Virus Removal Tool
ZoneAlarm Pro Antivirus + Firewall NextGen
VIPRE Antivirus - US And Others Countries, | India
Run A Full Scan And Delete/quarantine Detected Threats.
Win + R, Type temp → Delete All Files.Press Win + R, Type %temp% → Delete All Files.
Use Disk Cleanup: cleanmgr In The Run Dialog.
Go To: C:\Windows\System32\drivers\etc
Open hosts File With Notepad.
Replace With Default Content:
Press Ctrl + Shift + Esc → Open Task Manager
Go To Startup Tab
Disable Any Suspicious Entries.
Open Command Prompt As Administrator.
Run These Commands:
netsh Winsock Reset

netsh Int Ip Reset

ipconfig /flushdns
Unwanted Homepage Or Search Engine
Pop-ups Or Redirects
Unknown Extensions Installed
For Chrome:
Go To: chrome://extensions/
Remove Anything Unfamiliar
For Firefox:
Go To: about:addons → Extensions
Remove Suspicious Add-ons
For Edge:
Go To: edge://extensions/
Uninstall Unknown Add-ons
Chrome:
Go To chrome://settings/reset → "Restore Settings To Their Original Defaults"
Firefox:
Go To about:support → "Refresh Firefox"
Edge:
Go To edge://settings/resetProfileSettings → "Reset Settings"
All Browsers:
Use Ctrl + Shift + Del → Select All Time
Clear Cookies, Cached Files, And Site Data
Make Sure They Are Not Hijacked.
Chrome: chrome://settings/search
Firefox: about:preferences#search
Edge: edge://settings/search
Chrome: chrome://settings/cleanup
Use Malwarebytes Browser Guard For Real-time Browser Protection.
Always Download Software From Trusted Sources.
Keep Windows, Browsers, And Antivirus Updated.
Avoid Clicking Suspicious Links Or Ads.
Use ad Blockers And reputable Antivirus Software.
Backup Your Files Regularly.
To Remove Malware From Your Windows PC, Start By Booting Into Safe Mode, Uninstalling Suspicious Programs, And Scanning With Trusted Anti-malware Tools Like Malwarebytes. Clear Temporary Files, Reset Your Network Settings, And Check Startup Apps For Anything Unusual.
For web Browsers, Remove Unwanted Extensions, Reset Browser Settings, Clear Cache And Cookies, And Ensure Your Homepage And Search Engine Haven’t Been Hijacked. Use Cleanup Tools Like Chrome Cleanup Or Browser Guard For Added Protection.
?? Prevention Tips: Keep Software Updated, Avoid Suspicious Downloads, And Use Antivirus Protection Plus Browser Ad Blockers. Regular Backups Are Essential.
Why It Matters: Not All VPNs Offer Malware Protection.
What To Look For: Providers With built-in Malware/ad/tracker Blockers (e.g., NordVPN’s Threat Protection, ProtonVPN’s NetShield).
Purpose: Prevents Data Leaks If Your VPN Connection Drops.
Benefit: Ensures Your Real IP And Browsing Activity Aren’t Exposed To Malware-distributing Websites.
Why It Matters: DNS Leaks Can Expose Your Online Activity To Attackers.
Solution: Enable DNS Leak Protection In Your VPN Settings Or Use A Secure DNS Like Cloudflare (1.1.1.1).
Risk: Free VPNs Often Contain Malware, Sell User Data, Or Lack Security Features.
Better Option: Use Reputable Paid VPNs That Offer security Audits And Transparent Privacy Policies.
Some VPNs Block Known Phishing And Malicious Sites.
Example: Surfshark’s CleanWeb, CyberGhost’s Content Blocker.
Reason: Security Patches Fix Known Vulnerabilities.
Tip: Enable Auto-updates Or Check For Updates Weekly.
Scope: Malware Can Enter Through Phones, Tablets, Or IoT Devices.
Solution: Install VPN Apps On Every Internet-connected Device.
Fact: VPNs Do Not Remove Or Detect Malware On Your System.
Complement It With:
Antivirus Software
Firewall
Browser Extensions For Script Blocking
VPN Encrypts Traffic But Can’t Stop Malware From Executing If You Download Infected Files.
Split Tunneling Allows Certain Apps/sites To Bypass VPN.
Tip: Never Exclude Browsers, Email Clients, Or Download Managers From VPN Tunneling.
A VPN (Virtual Private Network) Enhances Your Online Privacy By Encrypting Your Internet Traffic And Masking Your IP Address. It Protects Your Data On Public Wi-Fi, Hides Browsing Activity From Hackers And ISPs, And Helps Bypass Geo-restrictions. VPNs Also Add A Layer Of Defense Against Malware By Blocking Malicious Websites And Trackers When Using Advanced Features. However, A VPN Does Not Remove Existing Malware Or Act As Antivirus Software. For Full Protection, Combine VPN Use With Antivirus Tools, Regular Software Updates, And Cautious Browsing Habits. Always Choose A Reputable VPN Provider With Strong Security And Privacy Policies.
Warlock Ransomware, Remove Warlock Ransomware, Delete Warlock Ransomware, Uninstall Warlock Ransomware, Get Rid Of Warlock Ransomware, Warlock Ransomw